A system can be technically ready and the organization can still be unready to launch it. I have seen programs reach go-live with infrastructure stable, deployment rehearsed and critical defects closed, only to discover that training is incomplete or the support model still depends on one key person. Go-live is often treated as the final technical checkpoint in delivery. In practice, it is a decision about whether the organization can absorb the change and operate through what follows.
The technical team can be ready while the business is not
The technology team may be confident that the system can be deployed. The business still has to decide whether it can operate effectively once that deployment is complete. A workaround may be technically acceptable and completely impractical at production volume. Data can pass reconciliation checks while business users still do not trust it. I have seen readiness meetings where every technical workstream reports green and one business owner quietly admits that only the straightforward scenarios have been tested. That one comment can be more useful than twenty pages of readiness metrics.
Programs often protect the launch date by shifting risk into operations
A defect is not fixed, so a manual workaround is introduced. Testing is shortened, training is reduced and support teams are asked to watch for issues after launch. The program appears to have reduced delivery risk. In reality, the risk has moved to operations, customer service, finance or frontline teams. That transfer may be reasonable if leadership understands it. The problem begins if the workaround is treated as though the issue has disappeared. A better discussion asks who will absorb the consequence, for how long and at what cost.
Problems that were left unresolved earlier usually show up together near launch
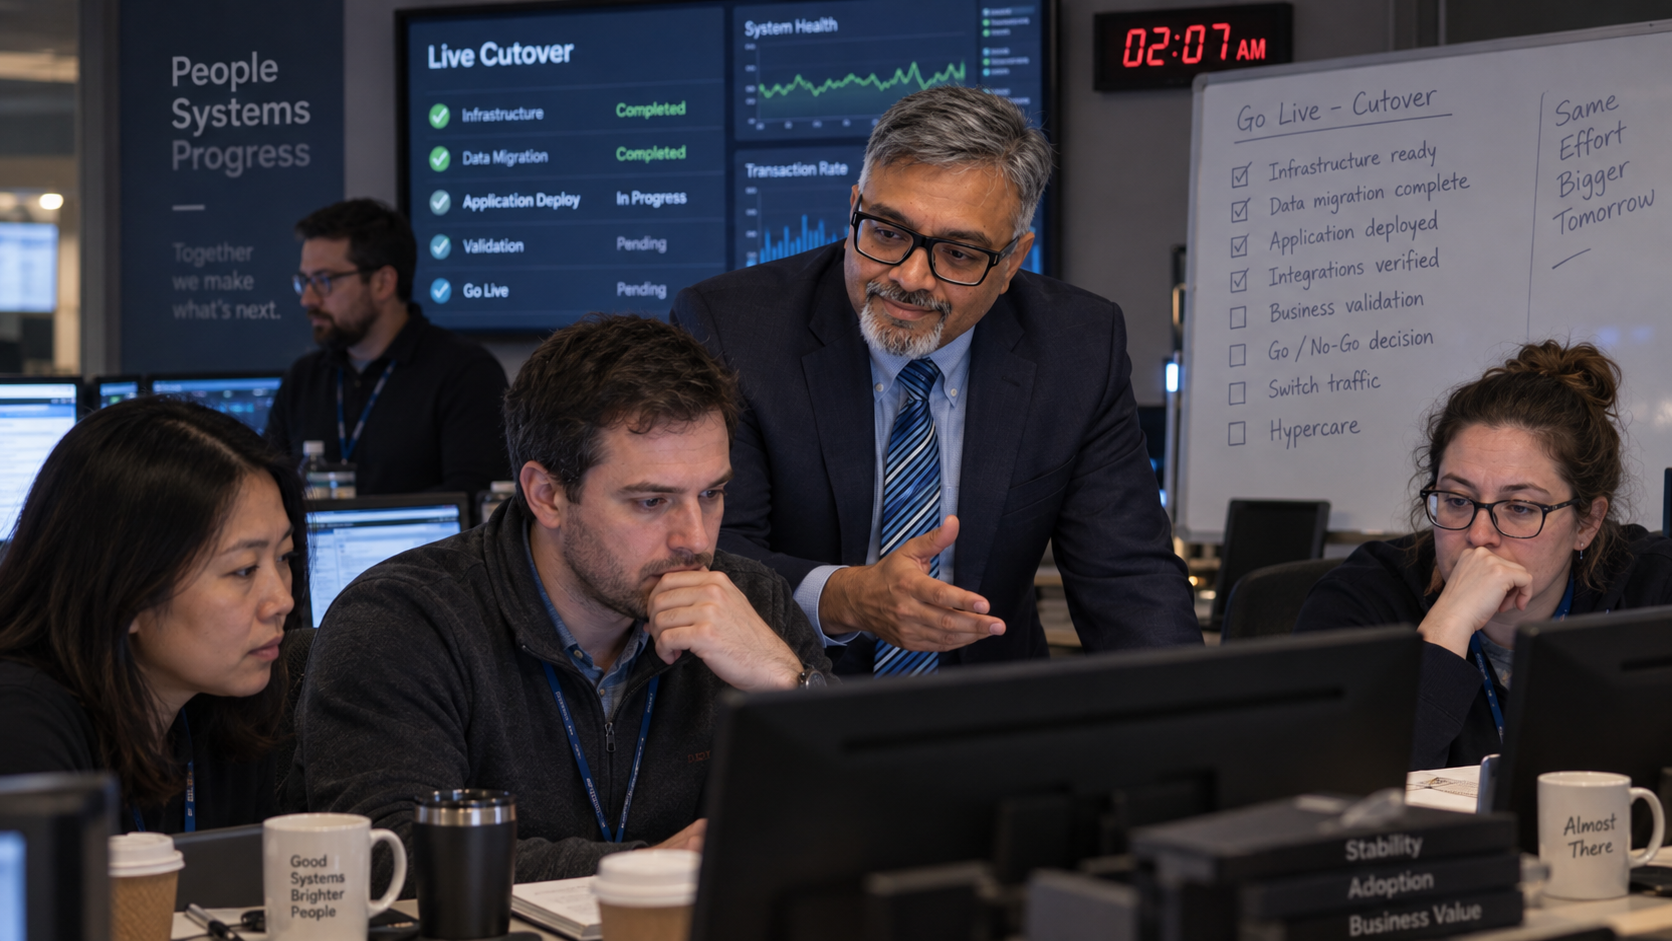
Launch pressure rarely appears from nowhere. It usually carries unresolved decisions from earlier in the program. Training was delayed because the solution kept changing. Data quality was accepted as good enough for now, and a dependency remained open because nobody wanted to escalate it too early. Near go-live, those issues arrive together. The team is closing defects, validating data, preparing support and still answering questions that should have been settled weeks earlier. I pay close attention to issues that have survived several reporting cycles. Their age often tells you more about ownership than their status colour does.
A no-go decision gets more expensive the later it is made
A no-go decision made two weeks before launch is inconvenient. The same decision made the night before cutover can be extremely expensive. Vendors may already be mobilized, communications may have gone out and operational teams may have reorganized around the date. A delay at that point carries more cost and more reputational impact. Readiness issues need to surface early enough for leadership to retain choices. If half the user population is still untrained three weeks before launch, the organization has options; forty-eight hours before launch, those options are much narrower.
Smaller organizations can mistake familiarity with the solution for readiness
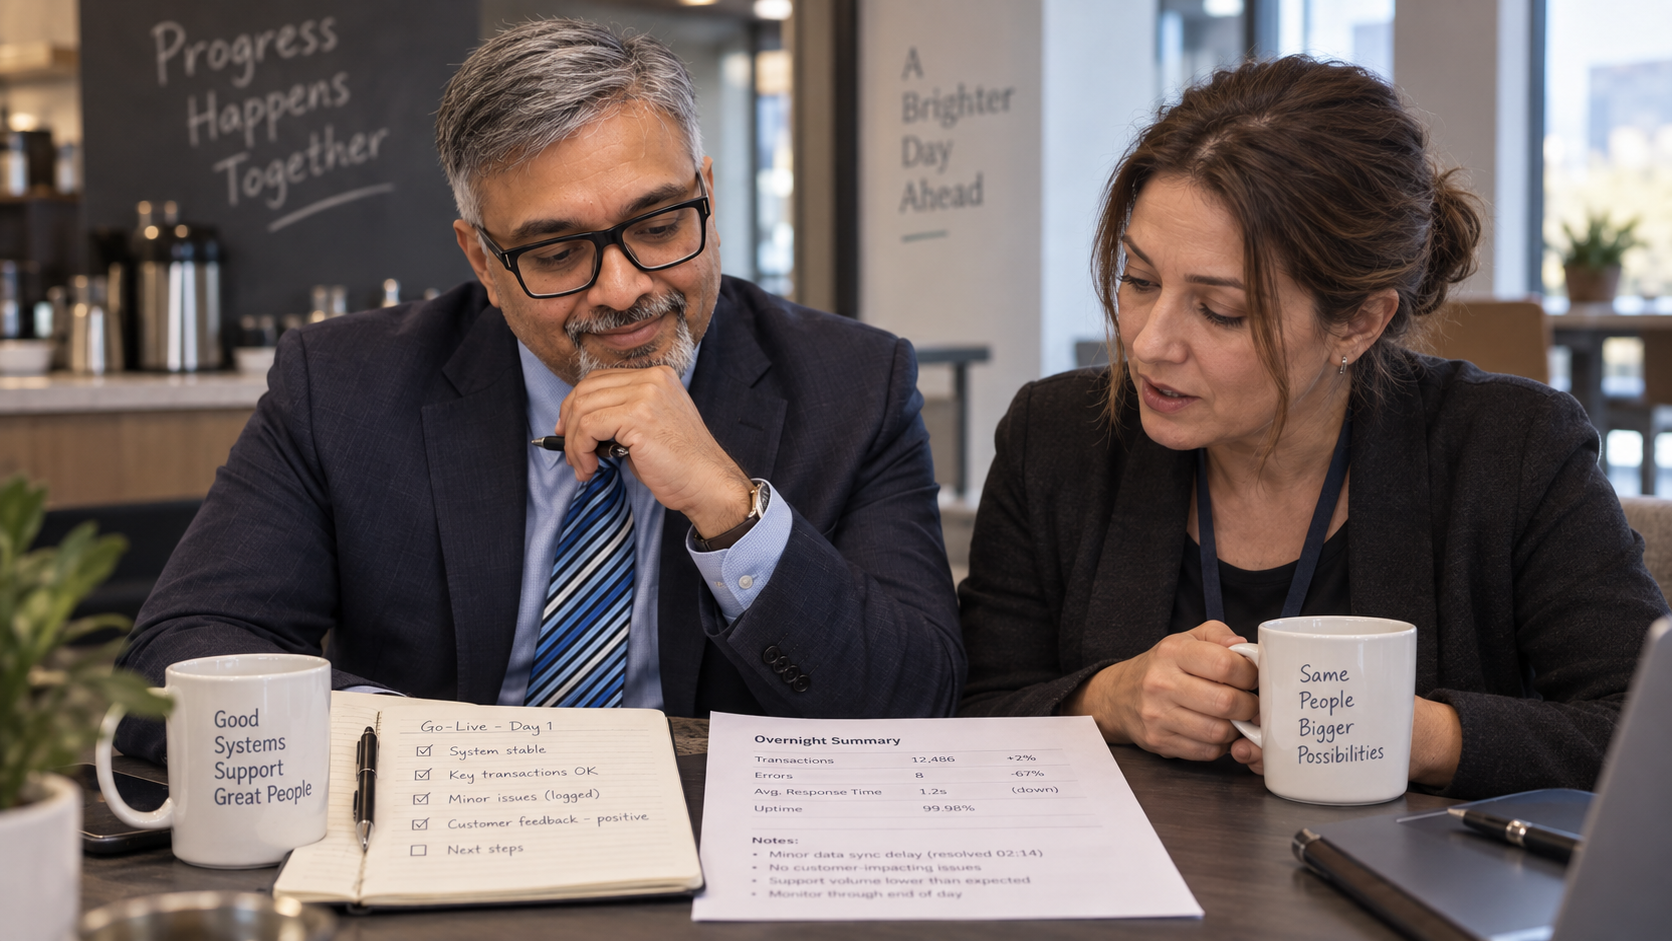
Smaller organizations often decide quickly because the people building, funding and operating the solution know each other closely. That can create confidence based more on familiarity than evidence. The founder may also be the sponsor, product owner and escalation point. The senior developer may know every workaround, and the operations lead may have been involved in every design discussion. Then the system reaches people outside the core team. What felt obvious becomes confusing, and the same small group becomes the unofficial support model. That is a readiness problem even if the technology works exactly as designed.
Large organizations can produce a lot of readiness evidence and still leave the main risk unclear
Large enterprises usually have many readiness artifacts. Technology, security, service management, data, training and business teams each have their own sign-offs. The volume of evidence can create confidence while leaving one question unanswered: what could materially disrupt operations on day one, and who owns that exposure? I have seen meetings spend more time debating whether a status should be amber or green than discussing the consequence behind the colour. A better question is who experiences the problem first if the organization launches with the issue still open.
The final go-live decision belongs to leadership
Technical teams can certify what they know. Business owners can explain operational exposure, and program leaders can present open issues and contingency plans. Someone still has to decide whether the remaining risk is acceptable. That is a leadership decision. The decision should not be framed as whether everything is complete. Very few launches are risk-free, and the useful question is whether the organization understands the remaining exposure and is prepared to own it. I would ask an executive team one question: are we prepared to own what happens after we turn it on?